Cyberattack alters freezer settings at French blood sites
The Établissement français du sang says staff fixed or moved products after remote settings changed; no health impact or lost blood products were reported.
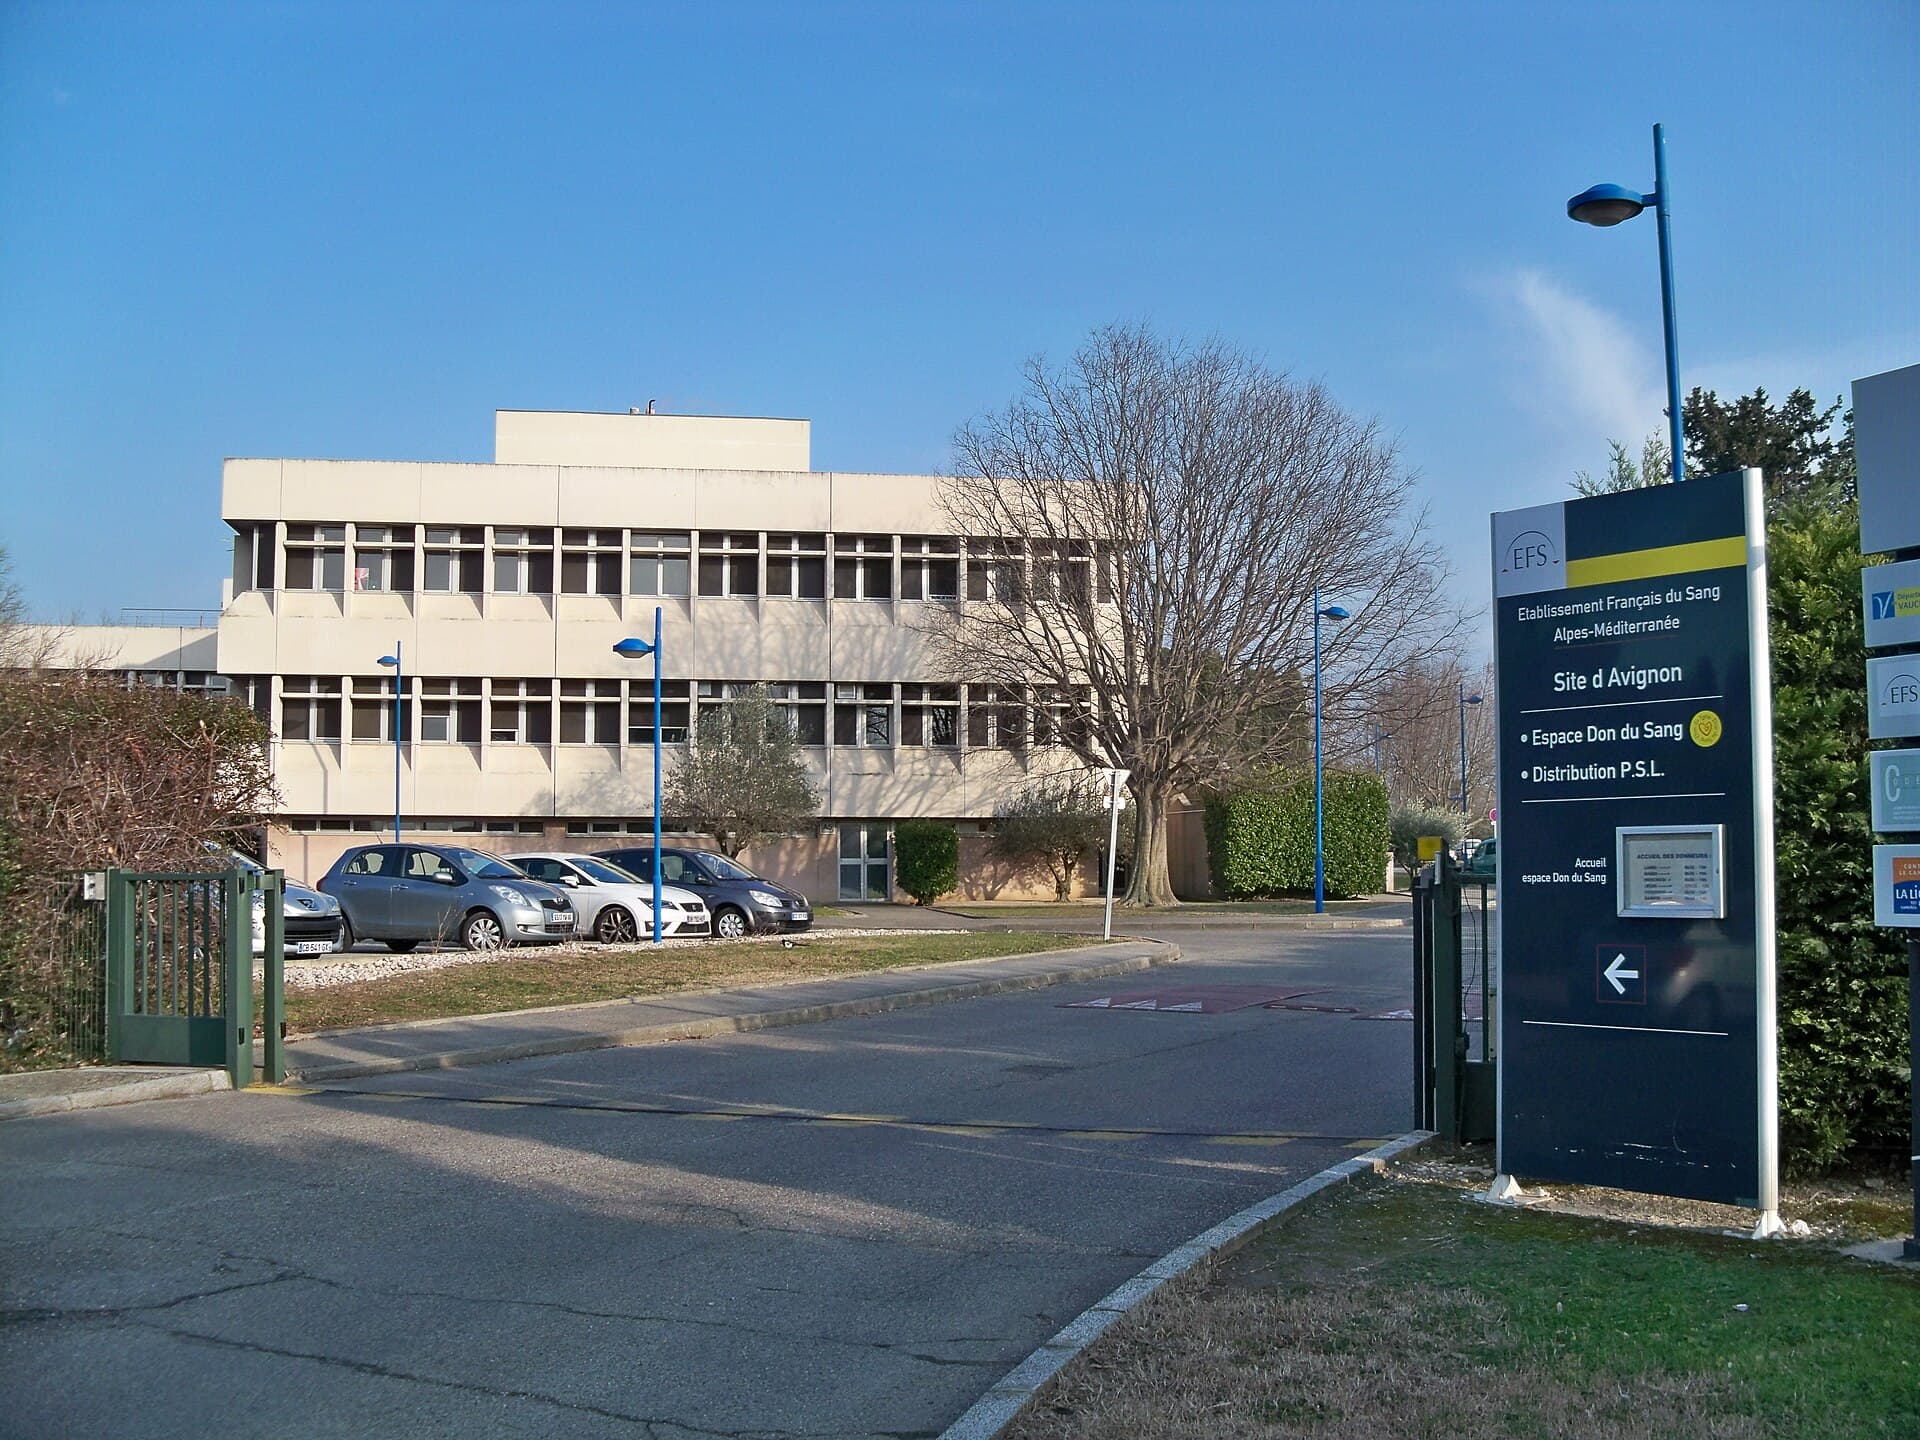
France's national blood service, the Établissement français du sang (EFS), confirmed that a cyberattack against one of its refrigeration equipment suppliers altered temperature and defrost settings at three cold-storage sites, BleepingComputer reported. EFS said the incident occurred on November 2 and that it was not the direct target. IO+ dated the confirmed cyberattack to November 1.
EFS did not name the supplier, according to BleepingComputer. Coolworld Rentals later said a cybersecurity incident involving remote monitoring software affected a limited number of its refrigeration units. Coolworld said the exploited vulnerability was in a third-party component outside its direct control and that it "responded promptly and took appropriate measures."
BleepingComputer wrote that the cold-storage chambers' temperature and defrost thresholds were set extremely high. EFS said its monitoring and alarm systems detected the change quickly, and staff fixed affected equipment or transferred products to other refrigeration facilities.
In a translated statement, EFS said: "No health impact has been identified, and no loss of blood products has been reported." The service added that plasma bags for transfusions and plasma for medicines were moved or secured, and that blood collection and distribution were not interrupted.
EFS said its technical teams were coordinating with France's national cybersecurity agency ANSSI and the Ministry of Health and had increased monitoring of refrigeration equipment and temperatures.
BleepingComputer reported that in October, about 250 to 350 French supermarkets were affected, among them Intermarché, Carrefour Market, Monoprix, Leclerc, and Super U. The targeted equipment included Danfoss and Copeland/Dixell controllers, and some systems ran older Danfoss software. This month a second wave hit more than 115 stores across Belgium, the Netherlands, Sweden, Luxembourg, Ireland, and Estonia. BleepingComputer said one Swedish supermarket's system reportedly began generating heat, and another store reported temperatures changed to 50°C (122°F).
IO+ wrote that the attacks spread across at least 11 European countries, and that France's CERT-FR had told organizations to cut public internet access and use secure VPNs for remote access. More than 2,765 Danfoss refrigeration systems remained exposed, IO+ reported.
The U.S. Cybersecurity and Infrastructure Security Agency earlier disclosed two Danfoss AK-SM 8xxA controller flaws, CVE-2025-41450 and CVE-2025-41451, that could let attackers bypass authentication and run commands remotely. BleepingComputer said it has not been confirmed whether these flaws are being exploited.
Cybersecurity Insiders wrote that the blood-service disruption raised concerns about hospital blood supplies and that disruptions could potentially continue for several days or weeks depending on damage and recovery. EFS has not reported such a timeline; it said operations continued without interruption.
Sources
Kai Brennan covers cloud providers, outages and vendor pricing for Five Nines. He writes from status pages, vendor announcements and published reporting.
Corrections. Report an error to corrections@thefivenines.com. We list substantive corrections on the corrections page.