Crédit Mutuel Arkéa hit by $133 million fraudulent transfers
The attacker used the bank's own account through a service provider's platform, not customer accounts, and converted funds into cryptocurrency, the bank said.
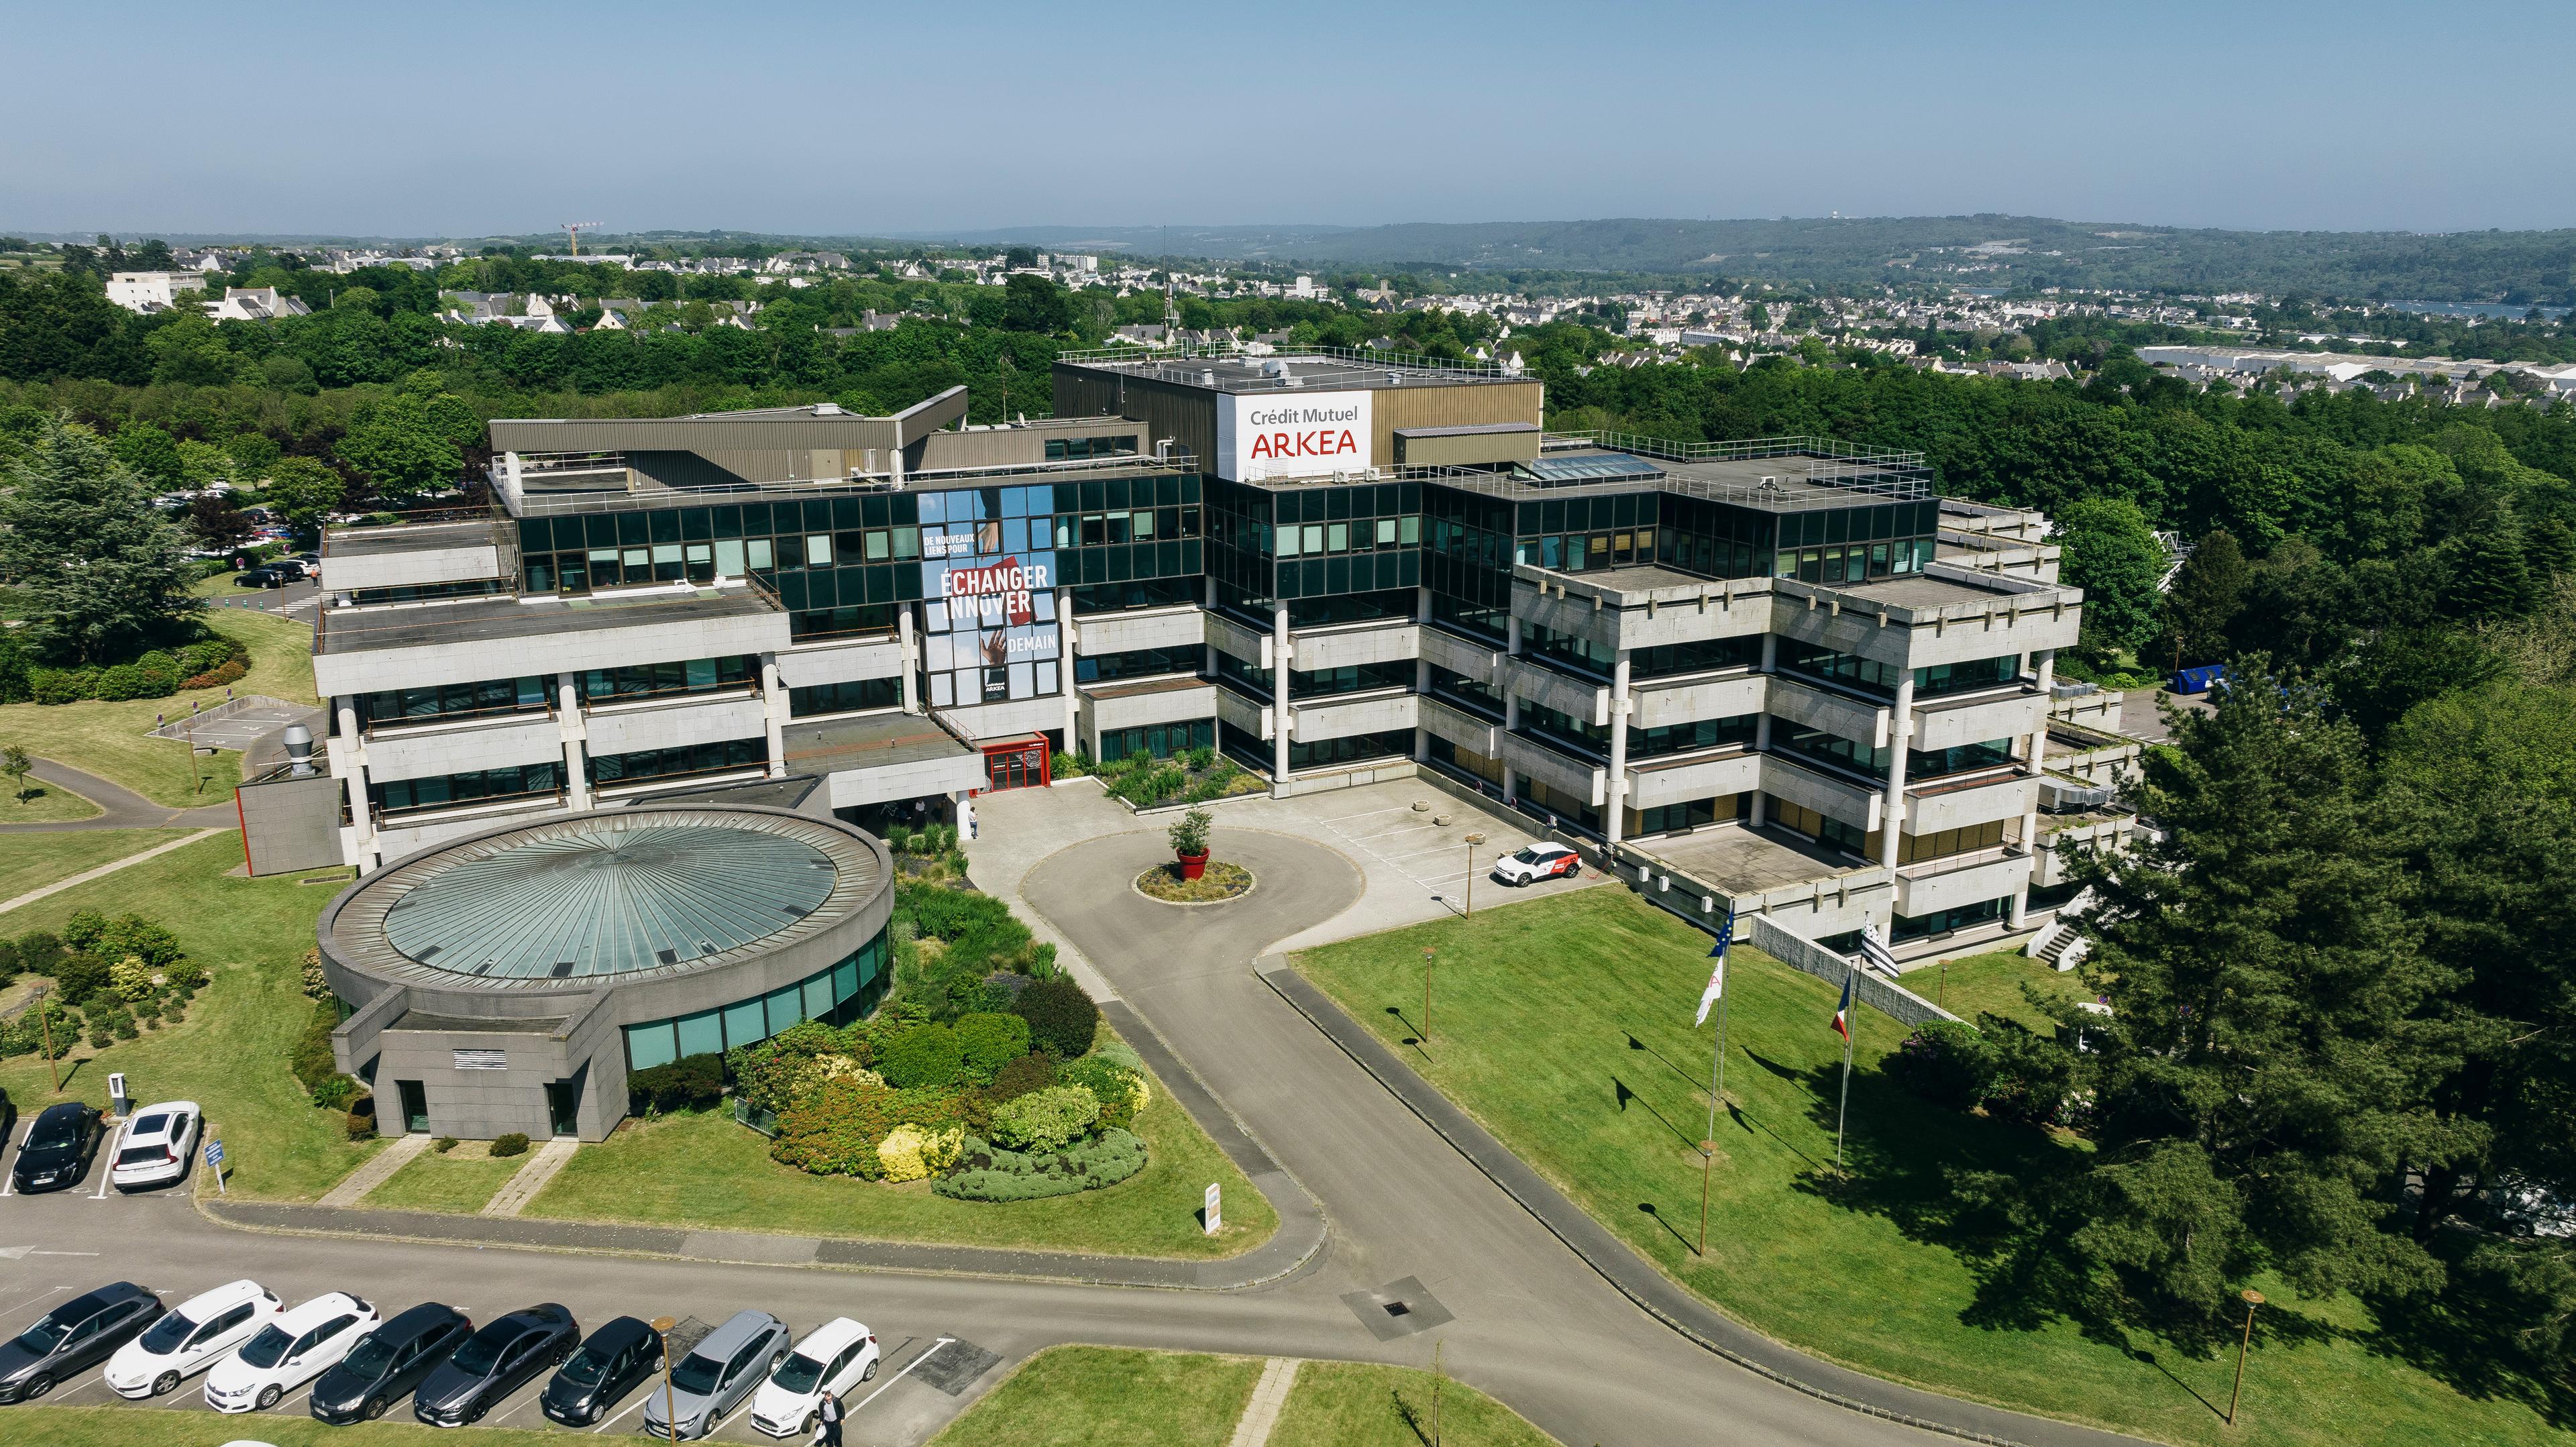
Crédit Mutuel Arkéa, a French cooperative bank that counts more than 5.8 million members and holds 211.5 billion euros in assets, said on November 4 that it was the target of a cyberattack, BleepingComputer reported. The bank said the incident "is now closed and under control." Blockchain fraud investigator ZachXBT had earlier reported that up to 118 million euros ($133 million) may have been stolen and withdrawn as USDC and USDT stablecoins.
The attacker used the bank's own account, not customer accounts, to carry out transactions with other banks and turn funds into cryptocurrency, the bank said in a FAQ. The attacker reached the network directly through a service provider's platform; Crédit Mutuel Arkéa ruled out Fortuneo. The bank also said it suspended certain systems in response.
ZachXBT reported on November 2 that a large, unauthorized withdrawal had taken place from several centralized exchange accounts the day before. By November 3, the lack of public disclosure had allowed $30 million to be laundered, the investigator said.
The bank did not confirm ZachXBT's figure. Asked whether 118 million euros ($133 million) were stolen, the bank said: "We do not confirm this information and can only validate the order of magnitude." The bank described the attack as a "sophisticated attack," said that human error at the bank was not the cause, and said it was working with judicial authorities and police.
Crédit Mutuel Arkéa assured customers that the incident "has no impact on their assets" and only delayed some transfer transactions. It warned of increased phishing risk and advised customers to verify suspicious messages by calling their bank adviser directly. BleepingComputer contacted the bank for more details but had not received a response at the time of publication.
Sources
- Hackers pull off $133 million French bank heist via service provider, BleepingComputer
Lena Vasquez covers vulnerabilities, breaches and identity for Five Nines. She writes from advisories, vendor bulletins and published reporting.
Corrections. Report an error to corrections@thefivenines.com. We list substantive corrections on the corrections page.