Sentry patches SDK flaw that skipped middleware
The flaw affects Next.js apps built with webpack when tunnelRoute is set, and middleware is the only authorization check.
Sentry has published a GitHub advisory for CVE-2026-114139, which affects the Sentry JavaScript SDK when used with Next.js middleware [1]. Patched versions are 9.47.2, 10.75.2, and 11.0.0-rc.1 [1].
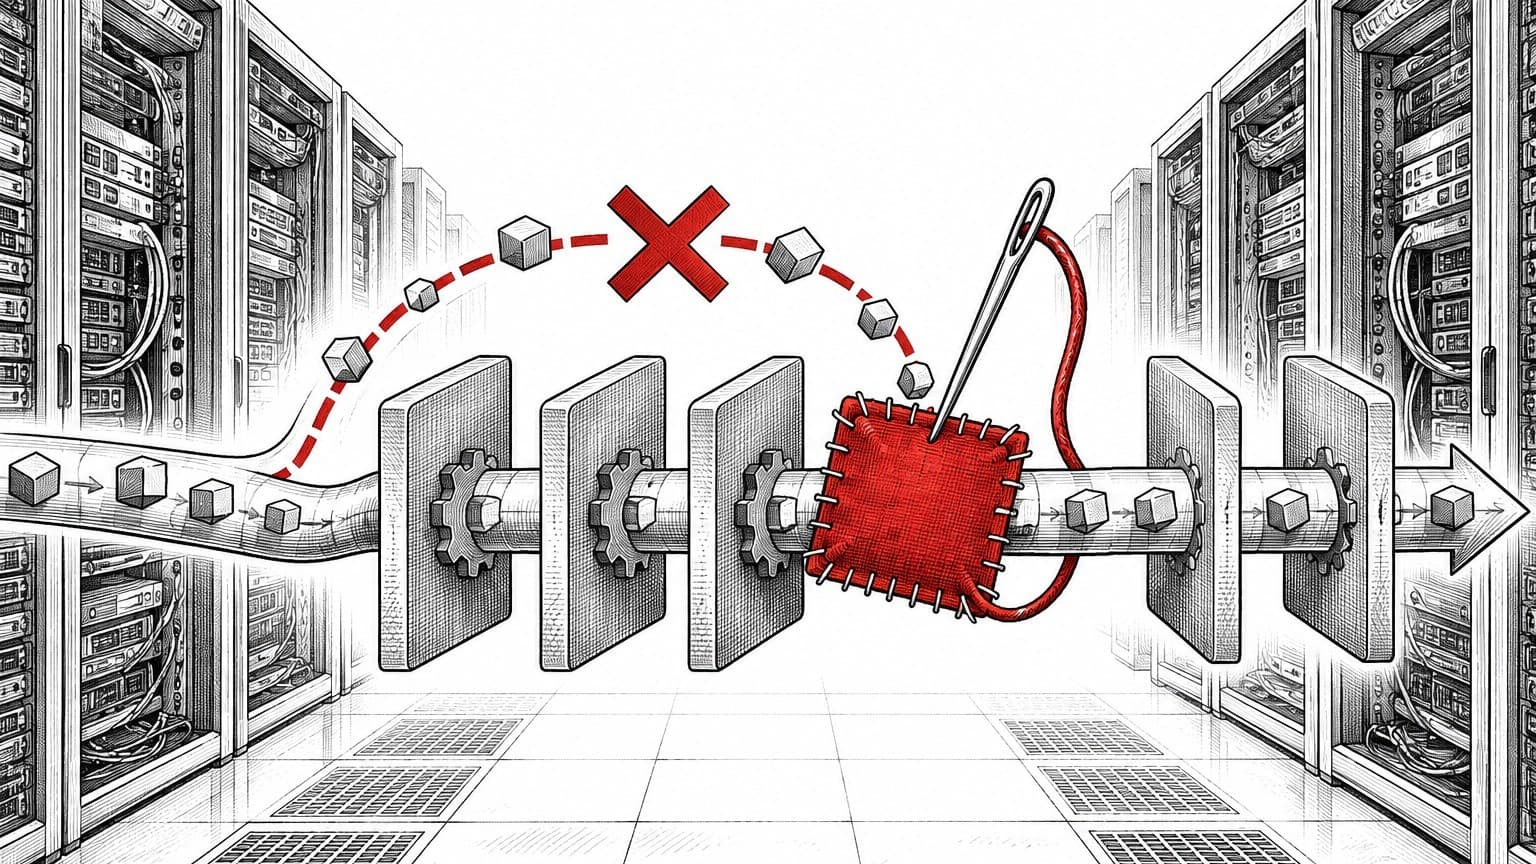
The flaw involves the tunnelRoute option. That option directs browser events to a path on the user's own Next.js server, and a rewrite there passes them to Sentry to bypass ad blockers [1]. To stop middleware from rejecting those envelope requests, the SDK skips middleware for them [1]. However, the rewrite only serves the tunnel path itself when the o and p parameters are set, while the skip applied to anything under that path [1]. Requests in that gap go to the application rather than Sentry, and middleware never runs on them [1].
The advisory lists four conditions that must all be true for a user to be affected: tunnelRoute is set, the app is built with webpack, some route resolves under the tunnel path, and middleware alone enforces authorization for those routes [1]. Turbopack builds are not affected [1]. Skipping middleware does not grant requests any privileges, and routes that check the session server-side remain protected [1].
Sentry's own services and data in Sentry organizations are not affected [1]. The fix limits the skip to exactly the requests that the tunnel rewrite handles, and no configuration change is needed [1]. As workarounds, the advisory suggests setting tunnelRoute to a path no route can resolve under, removing the option, building with Turbopack, or enforcing authorization in the route, layout, or data-access path in addition to middleware [1].
Sources
Lena Vasquez covers vulnerabilities, breaches and identity for Five Nines. She writes from advisories, vendor bulletins and published reporting.
Corrections. Report an error to corrections@thefivenines.com. We list substantive corrections on the corrections page.