CISA adds Arista VeloCloud Orchestrator SQL injection flaw to exploited list
Federal civilian agencies must remediate the flaw by Oct. 26 and check for compromise because CISA has evidence the bug is under active exploitation.
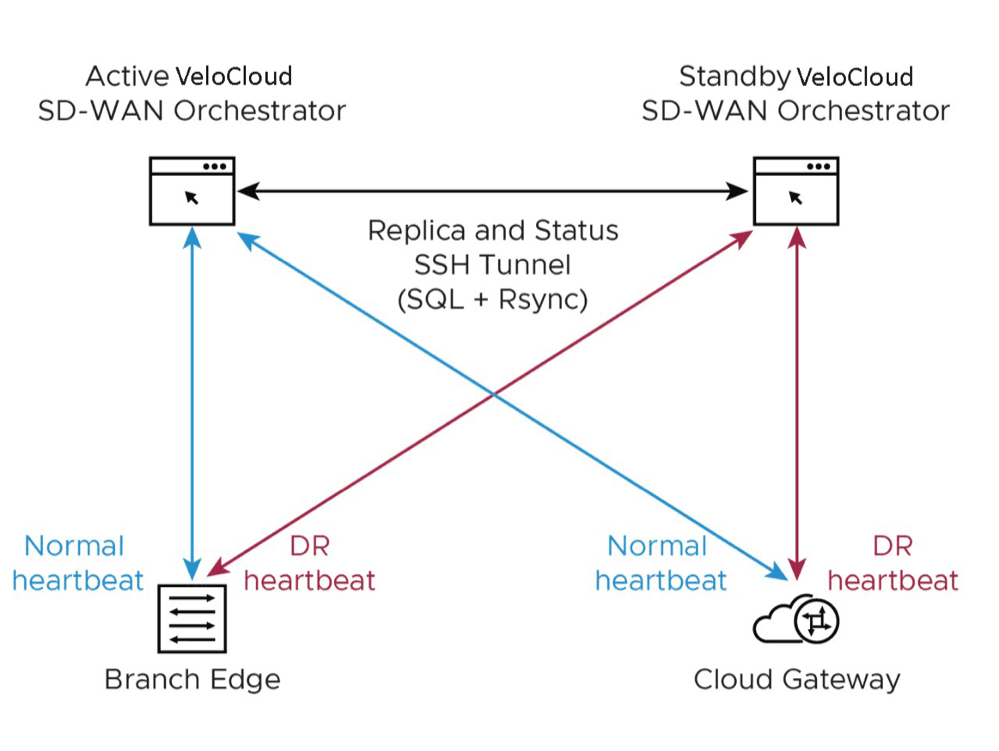
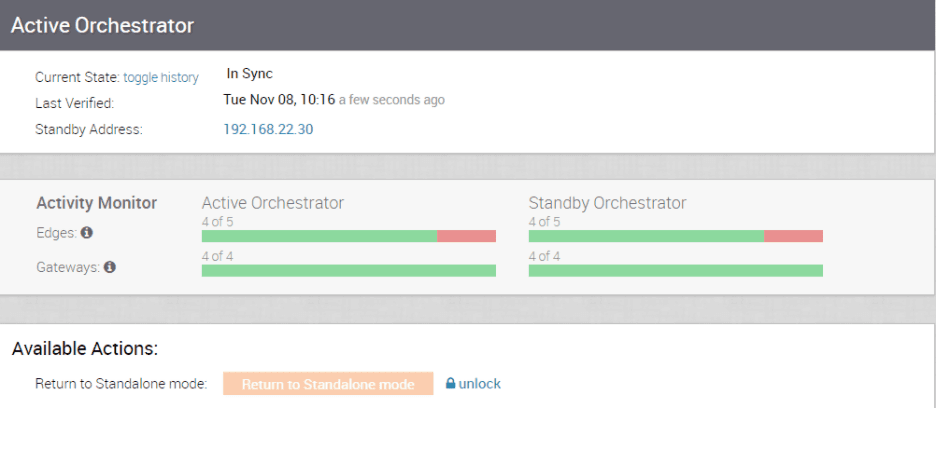
CISA maintains the Known Exploited Vulnerabilities catalog as an authoritative list of flaws exploited in the wild and tells organizations to use it when setting patching priorities. The agency added CVE-2026-114625 to that catalog on Oct. 23, 2026, after seeing evidence that the Arista VeloCloud Orchestrator SQL injection flaw is under active exploitation. The entry says the on-premises product may let a remote attacker reach privileged internal functions and affect the VCO host. A successful attack could weaken confidentiality, integrity, and availability for the orchestrator and the data it manages.
CISA's alert describes SQL injection as a common entry route for malicious actors and a serious risk to federal systems. The agency tied the addition to Binding Operational Directive 26-04, which requires Federal Civilian Executive Branch agencies to prioritize rapid fixes for high-risk vulnerabilities. Under that directive, KEV entries on publicly exposed assets that give an attacker total control after exploitation get priority over lower-risk flaws. The directive also sets when agencies must check whether a threat actor compromised the system before the patch was applied. The catalog lists Oct. 23, 2026, as the date the entry was added and Oct. 26, 2026, as the remediation due date for FCEB agencies. It flags the CVE as requiring forensic triage, aligning with that requirement. CISA has not determined whether attackers have used the flaw in ransomware campaigns.
BOD 26-04 is mandatory only for FCEB agencies, but CISA recommends that all organizations adopt risk-based vulnerability management and give KEV entries priority. The catalog action tells defenders to apply mitigations in line with vendor instructions, follow the cloud-service guidance in BOD 26-04, or stop using the product if no mitigation is available. Each organization should evaluate its asset's internet exposure and follow BOD 26-04 patching rules. The alert invites organizations to nominate known exploited flaws that are missing from the catalog.
Update, October 23, 2026
Arista disclosed the flaw in an advisory on October 22, The Hacker News reported. The vendor rated it 9.9 CVSS and said exploitation requires network access to the VCO web interface plus a valid login; even an Enterprise Read Only account can be escalated to local superuser, a role with full access. VCO is exposed by default, and no setting prevents that.
Fixed on-premises releases are 5.2.3.18, 6.1.3.10, and 6.4.2.12; hosted and dedicated orchestrators were already patched. Releases that fixed the July and September flaws remain vulnerable because they predate these versions. VeloCloud Gateway and Edge are not affected, and the 7.0 train is not vulnerable. This is the third VCO flaw Arista has reported as exploited since late July and the first that requires a login; the July CVE-2026-16812 and September CVE-2026-93952 flaws did not.
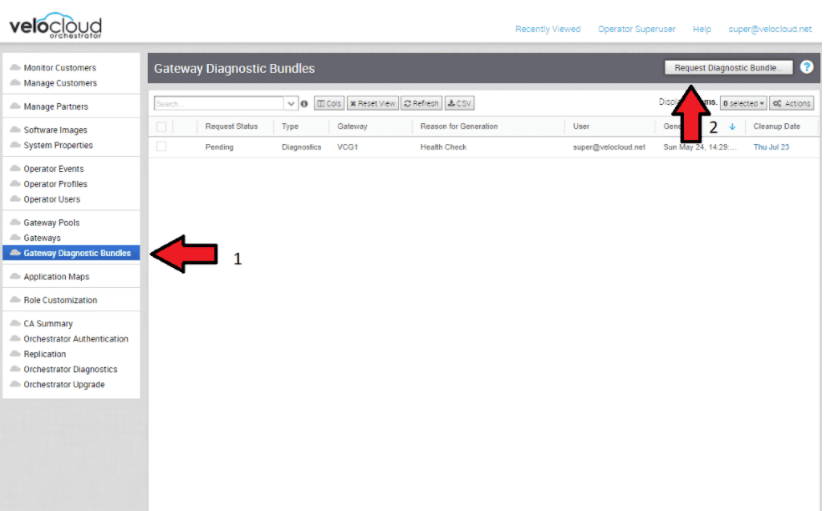
Arista named two IPs seen in attacks, 74.82.197[.]86 and 38.54.50[.]151, and said to block them and check logs. The company advised limiting VCO web access to trusted administrative networks, watching for backdoor daemons and webshells, and preserving logs before remediation. The advisory did not say when attacks began, which orchestrators were hit, or what attackers did after exploitation.
Sources
- Known Exploited Vulnerabilities Catalog | CISA, Cybersecurity and Infrastructure Security Agency CISA
- CISA Adds One Known Exploited Vulnerability to Catalog | CISA, Cybersecurity and Infrastructure Security Agency CISA
- Arista Warns of Critical VeloCloud SQL Injection Zero-Day Exploited in Attacks, The Hacker News
Noor Haddad covers attacks, breach disclosures and exploited vulnerabilities for Five Nines. Noor writes from CISA and vendor advisories, SEC disclosures and published reporting.
Corrections. Report an error to corrections@thefivenines.com. We list substantive corrections on the corrections page.