Chrome extensions with 13.4 million installs hijacked searches
Socket researchers found 319 unlisted Chrome Web Store extensions that routed queries through operator-controlled servers to collect Bing and Yahoo referral payments.
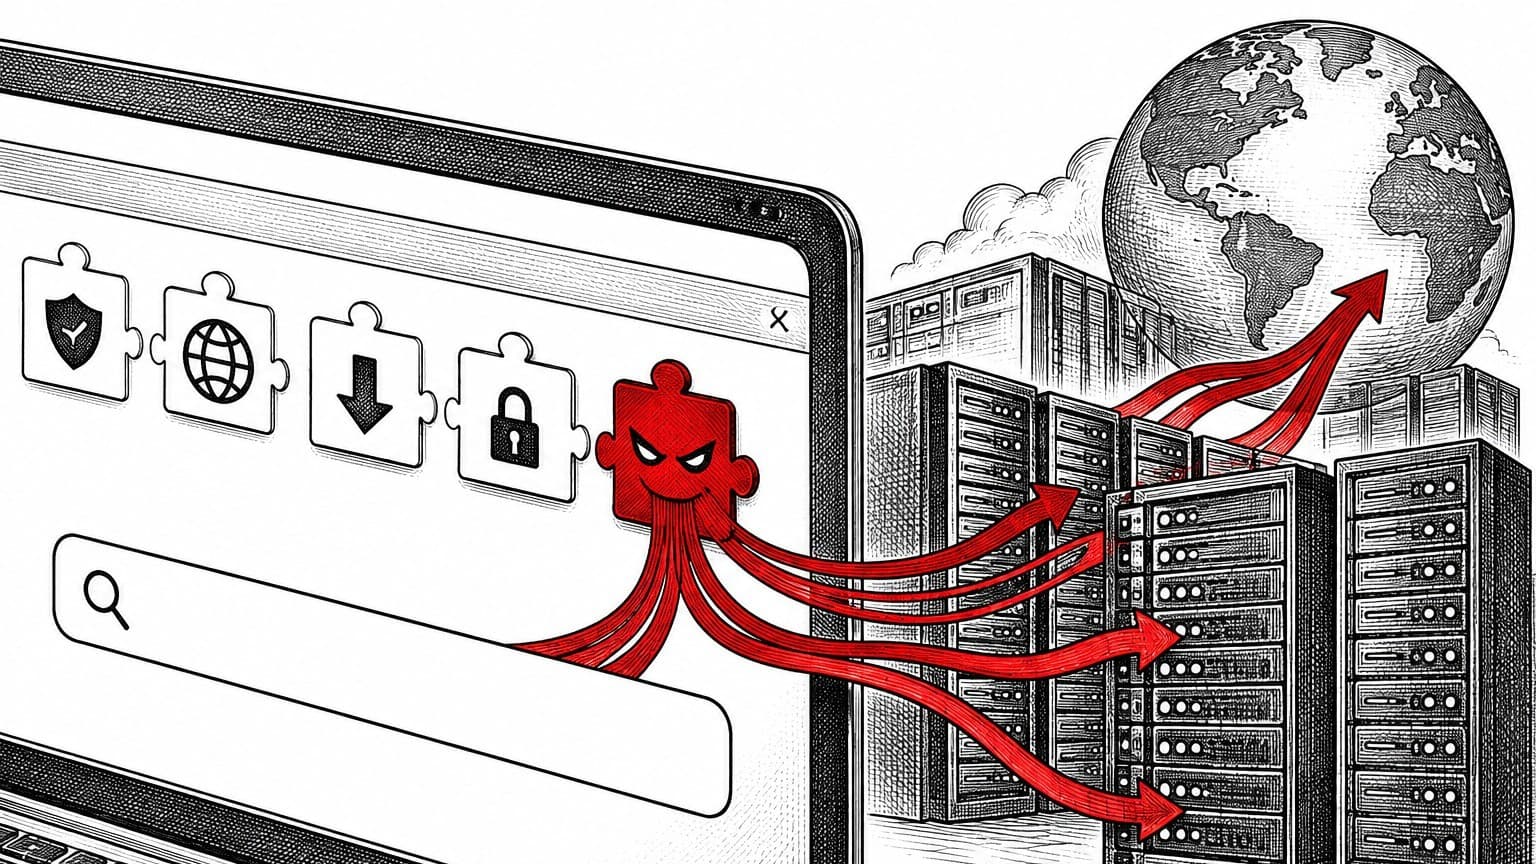
According to a report by Socket's John Tuckner, 319 Chrome extensions together drew 13.4 million reported installs and sent searches through operator-controlled servers to collect ad money from Bing and Yahoo.
The new report builds on Tuckner's April 2025 work, which had found 57 extensions with six million users, by adding 264 newly identified add-ons with another 8.7 million users.
Tuckner said the extensions were created by a small number of organized operators working from the same idea: "quietly take over the browser's default search engine, route every query through a suspicious proxy server, and collect partner referral payments from Yahoo or Bing under a syndication partner ID."
The add-ons present themselves as PDF converters, manual finders, safe search tools, and AI search tools. For the most part, they send search queries through a chain of pages until they land on Bing or Yahoo.
The Chrome Web Store hosts the extensions, but Socket says they are unlisted and do not show up when users search the store. Operators promote them through shady ads on websites instead.
Tuckner explained that many of these extensions need almost no code because Chrome's built-in setting called chrome_settings_overrides can replace the default search provider. One example includes only a manifest and icons and has no background scripts, content scripts, or permission requests.
Currently the extensions make money from search referrals by routing user queries through a server the operator controls before the query reaches Yahoo or Bing. But Tuckner said the final destination could be changed at any time with no extension update, including to phishing sites or malicious downloads. He said: "The search referral revenue is a profitable watering hole while the proxy operator can wait for data to accumulate and targets to surface before redirecting to malicious search results or landing pages for phishing or other malicious downloads."
Tuckner cited the Predator Search extension, which redirected him to four different sites when he performed six identical searches. When the same query was sent six times through its proxy server, the requests ended in four different places: Yahoo with partner tags, a landing page on searchlio.net, a second results domain reached through searchtosearch.com, and a Cloudflare error page. Tuckner reported: "The extension never changed; the proxy chose each destination as the search came in."
The largest recently active cluster, called "Bing-Search," has 37 extensions and 2.2 million users and is often promoted through Bidbrain ads. A separate "SecuryBrowse" wave has 58 extensions and 4.9 million users and promotes security-themed add-ons such as Fire Shield, Securify, and WatchTower.
Most of the extensions had already been removed from the Chrome Web Store when the report was published, according to Tuckner, though new ones keep being added.
BleepingComputer contacted Google for comment on Socket's findings, but the company had not responded by publication.
Sources
- Chrome extensions with 13.4 million installs caught hijacking searches, BleepingComputer
Noor Haddad covers attacks, breach disclosures and exploited vulnerabilities for Five Nines. Noor writes from CISA and vendor advisories, SEC disclosures and published reporting.
Corrections. Report an error to corrections@thefivenines.com. We list substantive corrections on the corrections page.